
Why are the standards and definitions of Industry 4.0 not clear?
A compatibility claim needs a document, a scope, and clear limits
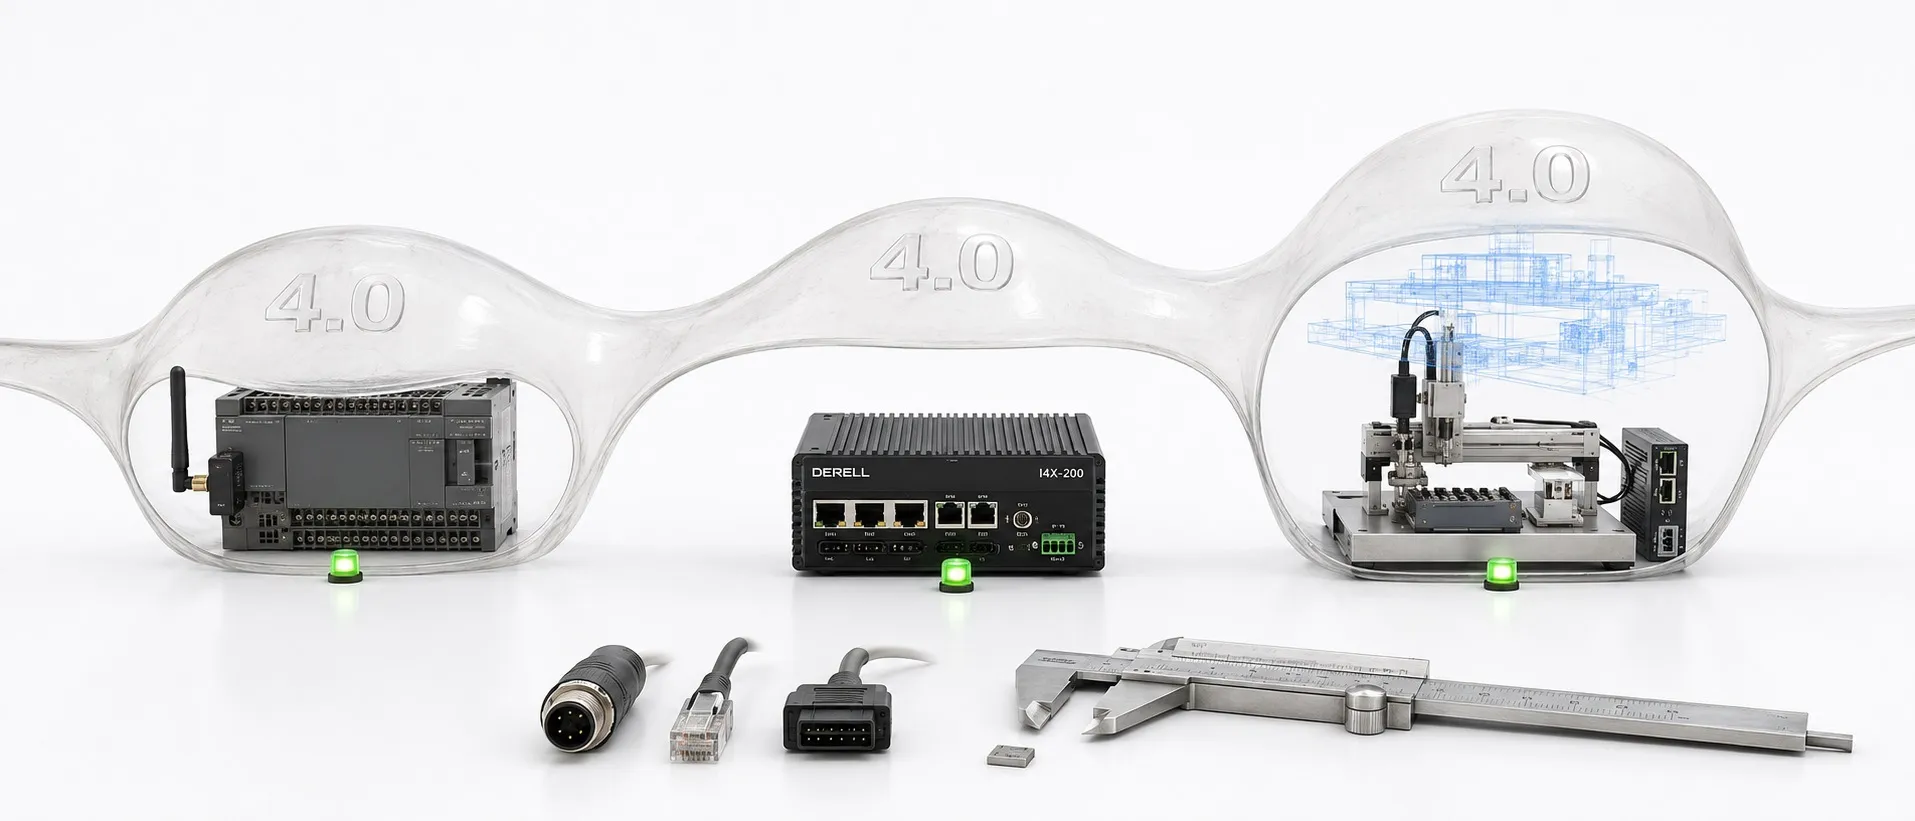
“Industry 4.0 ready” does not, by itself, explain which systems a device works with or which requirements it meets. The central problem with marketing language is its tendency to group different technical issues under one label of modernity. The uncertainty concerns what the general label guarantees, rather than every engineering rule. Keeping that distinction clear makes the criticism stronger.
It would also be inaccurate to say that no standards or definitions exist. Reference models, communication specifications, and security standards exist, but they address different matters. The existence of a document does not prove that every “4.0” product works with every other one. Ask the supplier to identify the document, version, and scope supporting the claim.
RAMI 4.0 is a reference model
DIN SPEC 91345:2016-04 defines the RAMI 4.0 reference architecture model. It provides a common framework for technical assets' life cycles and positions within a system. This model is not a test report demonstrating that two particular products work together.
A DIN SPEC is a publication type that does not require full consensus among all stakeholders. This does not make it worthless; it means that its publication type must be described accurately. A reference model, protocol, and product certificate are not interchangeable.
Concepts, device features, and project requirements operate at different levels
The Internet of Things and industrial IoT describe connected devices and the use of their data. The information exchanged between a PLC and a SCADA system depends on the selected hardware, software, versions, and configuration. “IoT enabled” leaves the technical requirement incomplete if it does not identify the interface and data structure being delivered.
A project requirement is more concrete: which measurements will be collected, how often will they update, and what happens if the connection fails? These answers should not be inferred from a general description in a brochure. Turn the need into a measurable delivery requirement.
Physical connections and communication protocols must be distinguished
An Ethernet port does not prove that devices interpret all application data in the same way. RS-485 is an electrical interface, rather than an application protocol defining the meaning of data. For a connection using Modbus RTU, device addresses, serial communication settings, and register information must also be known. A general claim of Modbus communication does not replace those details.
Devices supporting EtherCAT or PROFIBUS must likewise be assessed against the relevant system requirements. Seeing a protocol family's name does not prove that every device function is available to the other system. The same connector does not establish the same protocol, and the same protocol does not establish the same application.
Transporting data and conveying its meaning are different tasks
Assessing device compatibility requires more than checking that a connection opens. Measurement units, scaling, data types, and error representations also matter. A displayed value of “100” does not explain whether it means 100 °C, 10.0 bar, or an error code.
Exporting a file from a datalogger does not demonstrate that another program interprets it correctly. Data analysis needs preserved timestamps, channel names, and measurement conditions. Technologies such as OPC UA provide concrete mechanisms for information modeling and data access, while the models and functions used in a project still need specification.
A security standard is not a general “4.0 certificate”
Documents such as the IEC 62443 series address industrial cybersecurity. For example, IEC 62443-2-1:2024 addresses policies and procedures for an asset owner's security program for industrial control systems in operation. That scope is different from device data mapping or a project's economic success.
IoT device security must also be assessed through the features and installation in use. OPC UA offers encryption, authentication, and access control capabilities; their availability does not demonstrate correct configuration. A security feature or a document with a limited scope cannot be treated as a general guarantee for an entire plant.
A label does not establish measurement accuracy or acceptance criteria
For a sensor, range, accuracy, and output type matter. For an encoder, resolution, interface, and counting arrangement matter. Calling them smart does not replace these specifications. Electrical compatibility, data transfer, measurement accuracy, and operational requirements need separate verification within the same project.
Project success is not measured by counting standard names either. Reduced record loss, correct recipe transfer, or shorter downtime can be acceptance criteria. Record which trials were conducted with which devices and versions. A demonstrated function provides stronger evidence than a general compatibility slogan.
Questioning vague sales claims does not require guessing motives
Some quotations may offer hardware, software, and consulting packages with an unclear scope under an “Industry 4.0 transition” banner. Assess whether the package is needed through a cost and risk evaluation. However, presenting a claim that every supplier deliberately keeps standards vague as an established fact would be unjustified without evidence. The criticism should rest on missing technical explanations and claims that cannot be verified.
Editor's note: Using a standard, demonstrating conformity, and holding a certificate are different claims. If a certificate is provided, examine the product, version, and assessment scope it covers. Without a document reference, a defined scope, and test results, “Industry 4.0 ready” should be read primarily as a sales label rather than a technical explanation.
Related information pages
What is the Internet of Things?
What is industrial IoT?
What is a PLC?
What is SCADA?
What is Ethernet?
The RS-485 interface
Modbus communication
What is Modbus RTU?
What is EtherCAT?
What is PROFIBUS?
IoT device compatibility
Industrial cybersecurity
IoT device security
Measuring project success