
What security protocols are used in Ethernet networks?
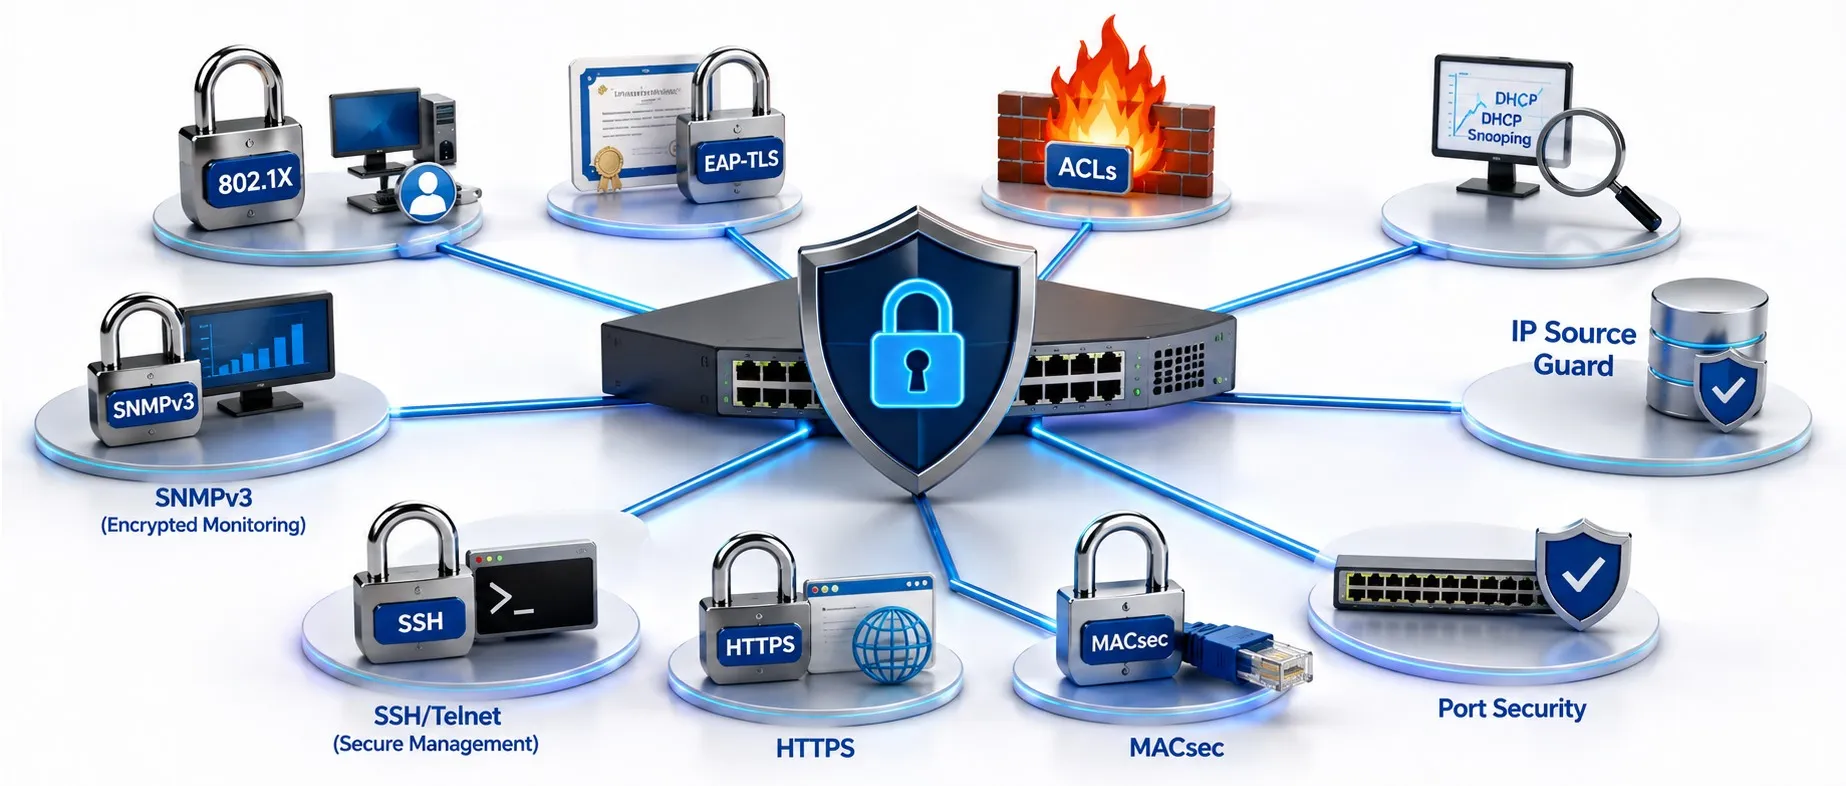
There is no single universal “Ethernet security protocol.” Ethernet networks are normally protected by several layers working together: IEEE 802.1X controls who may access a port, MACsec protects Layer-2 frames, IPsec protects IP packets, TLS protects application sessions, and industrial protocols can add their own security mechanisms.
This distinction matters in automation. Creating a VLAN does not automatically encrypt traffic between a PLC and an HMI. Adding a MAC address to a port-security list is not strong device authentication. Using TLS does not, by itself, stop an unauthorized device from plugging into an open switch port. Each control solves a different problem.
Ethernet security is built in layers, not by one universal protocol.
| Layer / function | Example | What it protects | What it is not |
|---|---|---|---|
| Port access | IEEE 802.1X / EAPOL | Prevents normal network access through a controlled port until a device or user is authenticated and authorized. | It does not encrypt all application data by itself. |
| Layer-2 data protection | IEEE 802.1AE MACsec + MKA | Can provide confidentiality, integrity and data-origin authenticity for Ethernet frames. | It is not an end-to-end routed IP tunnel. |
| Layer-3 protection | IPsec / ESP + IKEv2 | Protects IP packets in host-to-host, host-to-gateway or gateway-to-gateway scenarios. | It is not Ethernet switch-port authentication. |
| Application / transport security | TLS 1.3, DTLS, HTTPS | Protects a specific client/server or application session against eavesdropping, tampering and forgery. | It does not automatically encrypt the whole Layer-2 LAN. |
| Industrial protocol security | CIP Security, OPC UA Security, PROFINET Security | Adds device/message security appropriate to the industrial application protocol. | It is not automatically present on every Ethernet device. |
| Network architecture | VLANs, ACLs, firewalls, DMZs, port security | Limits which systems can communicate and reduces lateral movement. | These are not all encryption protocols. |
Is basic Ethernet encrypted by itself?
No. The basic MAC/frame functions described by the Ethernet protocol do not automatically guarantee confidentiality or cryptographic source authentication. An Ethernet frame carries source and destination MAC addresses and uses an FCS for transmission-error detection, but the FCS is not a cryptographic authenticity mechanism.
A practical way to separate the questions is: May this device join the LAN? → 802.1X; Should this Layer-2 frame be protected against reading and modification? → MACsec; Should this application or IP path be protected end to end? → TLS/IPsec or protocol-specific security.
IEEE 802.1X: who is allowed through the switch port?
IEEE 802.1X is port-based network access control. The current IEEE 802.1X-2020 material covers the use of EAP over LANs through EAPOL, controlled-port access and the MACsec Key Agreement mechanism. [1]
A typical deployment has three roles: the supplicant is the endpoint requesting access; the authenticator is the switch or access device controlling the port; and the authentication server evaluates credentials or policy. RADIUS is commonly used on that backend path.
802.1X should not be reduced to “username and password on a switch.” EAP can support different authentication methods, including certificate-based approaches. Also, many legacy PLCs, drives and sensors do not implement an 802.1X supplicant, so OT deployment has to be checked per device model.
What does RADIUS do?
RADIUS is an AAA protocol used to carry authentication, authorization and configuration information between a network access device and a central authentication server. RFC 2865 defines that client/server role. [2]
Because RADIUS and 802.1X are often deployed together, they are sometimes treated as the same protocol. They are not. EAPOL is used on the LAN access side between supplicant and authenticator; RADIUS is commonly used from the authenticator toward the backend AAA server. RADIUS is also not a protocol for encrypting normal Ethernet user traffic.
What is MACsec?
MACsec — IEEE 802.1AE provides MAC-layer security services including confidentiality, integrity and data-origin authenticity for Ethernet traffic. IEEE's current MACsec page explains that the MACsec Key Agreement protocol, MKA, is specified in 802.1X and distributes the keys used to protect frames. [3]
MACsec is useful because it protects Layer-2 traffic regardless of whether the payload is IP, TCP, UDP or another protocol. It can therefore be used on suitable switch-to-switch uplinks, server links or industrial Ethernet segments. Both endpoints and the network design must support it.
MACsec should not be confused with a routed end-to-end Internet tunnel. It protects controlled Ethernet connectivity at Layer 2; if protection must continue across routers or wider IP networks, IPsec or application-level TLS may be more appropriate.
Are 802.1X and MACsec the same thing?
| Feature | 802.1X | MACsec / 802.1AE |
|---|---|---|
| Main function | Authenticate and authorize access to the network port | Cryptographically protect Layer-2 Ethernet frames |
| Encryption | Not primarily user-data encryption by itself | Can provide confidentiality |
| Key management | Also specifies MKA | Uses Secure Association Keys established/distributed through MKA |
| Question answered | “Who may use this controlled port?” | “Can this Ethernet frame be read or modified on the link?” |
The technologies can complement one another: first authorize the endpoint, then protect the traffic with MACsec where the design and devices support it. [1]
TLS: protecting the application session
TLS (Transport Layer Security) is a cryptographic protocol designed to protect client/server communication from eavesdropping, tampering and message forgery. TLS 1.3 is specified in RFC 8446. [4] HTTPS is one of its most familiar uses.
TLS works at a different level from MACsec. MACsec protects Layer-2 frames; TLS protects a particular application session. On the same Ethernet LAN, a web interface may be protected by HTTPS/TLS while an older PLC protocol remains unencrypted. A TLS-capable switch therefore does not mean every packet on the LAN is encrypted.
Older documentation often says “SSL/TLS.” For new designs, the actual supported TLS version and cipher configuration should be verified from the device documentation instead of treating the terms as interchangeable.
When are IPsec and VPNs used?
IPsec is an IP-layer security architecture. RFC 4301 defines authentication, integrity, access control and confidentiality services for IP traffic. [5] In common deployments, ESP protects traffic while IKEv2 handles mutual authentication and the establishment and maintenance of Security Associations. RFC 7296 defines IKEv2 as an IPsec component. [6]
“VPN” is not one protocol name. A VPN product may use IPsec/IKEv2, TLS-based tunnelling or another technology. For OT remote access, simply saying “we have a VPN” is not enough: endpoint security, MFA, authorization, logging, jump hosts and the reachable OT zones still matter.
Is a VLAN a security protocol?
A VLAN is not an encryption or authentication protocol. VLANs create logical Layer-2 broadcast domains and can be valuable for segmentation. But if routing between VLANs is allowed by ACL or firewall policy, traffic can still pass between them.
That is why “the PLCs are in their own VLAN, so the network is secure” is incomplete. CISA recommends strong segmentation using router ACLs, stateful firewalls, DMZ constructs and VLAN/PVLAN separation as part of defense in depth. [7] In automation this belongs inside the broader industrial cybersecurity architecture.
Where do ACLs, firewalls, port security and DHCP snooping fit?
These are important security controls, but calling all of them “security protocols” is technically inaccurate.
| Mechanism | Main function | Limitation |
|---|---|---|
| ACL | Permit or deny traffic by address, protocol, service or port rules | Does not automatically encrypt allowed traffic. |
| Firewall | Enforce approved flows between zones or networks | Protection depends on correct rules and architecture. |
| Port security / MAC filtering | Limit which MAC addresses may appear on a switch port | MAC addresses can be spoofed; this is not strong authentication. |
| DHCP snooping | Restrict rogue DHCP behaviour and build binding information on supported switches | Does not encrypt application traffic. |
| Dynamic ARP Inspection / IP Source Guard | Validate ARP/IP source behaviour using switch-side policy/bindings | Switch feature, not end-to-end cryptographic identity. |
| IDS/IPS | Detect or block suspicious traffic and behaviour | Does not replace authentication, segmentation or encryption. |
Because a MAC address can be locally administered or changed, MAC allow-lists alone are a weak basis for device identity.
Why do SSH, HTTPS and SNMPv3 matter?
The management plane of industrial switches, firewalls, gateways and servers also needs protection. SSH can be used for encrypted command-line administration, HTTPS/TLS for web management, and appropriately configured SNMPv3 for authenticated/private network management. SSH Transport Layer Protocol is specified by RFC 4253 and the SNMPv3 User-based Security Model by RFC 3414. [8]
That is why an old diagram labelling “SSH/Telnet — Secure Management” is misleading. Telnet is not encrypted secure management. Likewise, SNMPv1/v2c community strings should not be treated as equivalent to SNMPv3 authentication/privacy.
What does CIP Security add to EtherNet/IP?
For automation systems using EtherNet/IP, CIP Security is ODVA's protocol/application security layer for CIP-connected devices. ODVA describes device authentication, message integrity/authentication, authorization and optional confidentiality. TLS can protect TCP-based EtherNet/IP communication, while DTLS can protect UDP-based real-time traffic; X.509 certificates or pre-shared keys can be used for endpoint trust. [9]
The presence of an EtherNet/IP port does not prove that a product implements CIP Security. Security profiles and product support must be checked at model and firmware level.
Is OPC UA security the same as Ethernet security?
OPC UA is not an IEEE 802.3 security protocol, but it is a good example of higher-layer security commonly used on Ethernet/IP networks. The OPC Foundation security model explicitly covers Client/Server authentication, user authentication, communication integrity and confidentiality. [10]
The model can use certificates, message signing and encryption. OPC Foundation also makes clear that the selected security mechanisms must be configured for the needs of the installation. In other words, “OPC UA is present” does not mean every deployment has the same security level.
How is PROFINET security evolving?
PROFINET now includes protocol-level security work in addition to the traditional segmentation/firewall model. The current PI roadmap lists PROFINET Security Classes 1/2/3 under today's technologies, while PROFINET Specification V2.5 introduces comprehensive security mechanisms, secure provisioning and a dedicated Security Profile. [11]
These features still depend on the actual product, firmware and conformance implementation. Replacing a switch does not magically give an older PROFINET device a newer security class.
What about EtherCAT?
With EtherCAT, functional safety and cybersecurity must remain separate concepts. FSoE and other safety mechanisms address hazardous machine behaviour; they are not authentication or encryption mechanisms against a malicious network actor. An EtherCAT machine network still needs controlled engineering access, segmentation and properly protected connections to upper-level networks.
What combination makes sense for a PLC network?
There is no universal recipe. A fixed production line might combine the following layers:
1. Keep PLCs, HMIs and drives in appropriate OT VLANs/zones.
2. Allow IT–OT traffic only through controlled firewall/DMZ paths.
3. Restrict engineering-station access by user/device identity and, where supported, 802.1X.
4. Evaluate MACsec for critical Layer-2 links when switches/endpoints support it.
5. Use supported current TLS configurations for SCADA, web interfaces and APIs.
6. Use IPsec/TLS VPN + MFA + an authorized jump-host model for remote access.
7. Enable protocol-specific security for EtherNet/IP, OPC UA or PROFINET where the devices support it.
8. Monitor authentication, switch counters, logs and anomalous network behaviour.
The goal is not to force the same technology everywhere. It is to build defense in depth so that one open port or compromised workstation does not provide unrestricted movement across the production network.
Common mistakes in plant networks
“We made a VLAN, so the traffic is encrypted.” No — VLANs provide segmentation.
“The MAC allow-list proves device identity.” No — MAC addresses can be spoofed.
“802.1X encrypts all traffic.” No — its main role is network access control.
“MACsec makes TLS unnecessary.” No — they protect different layers.
“We have a VPN, so the OT network is secure.” No — a VPN protects a path, not every endpoint or authorization decision.
“EtherNet/IP or PROFINET is automatically secure.” No — security profiles, firmware and configuration matter.
“FSoE is cybersecurity.” No — functional safety and cybersecurity have different objectives.
In one paragraph
Ethernet security is layered. 802.1X controls port access, MACsec protects Layer-2 frames, IPsec protects IP packets, and TLS protects application sessions. RADIUS is commonly used as the backend AAA service in 802.1X deployments. VLANs, ACLs, firewalls, DMZs and port security are important controls, but they are not all encryption protocols. In industrial networks, CIP Security, OPC UA Security and PROFINET Security add application-level protection when supported by the actual device. The strongest design combines these controls inside a broader industrial cybersecurity architecture.
Related Ethernet guides
What is Ethernet? • How does Ethernet work? • Ethernet protocol • Ethernet frame structure • MAC address • Ethernet card / NIC •