
what is SFF and HFT safety?
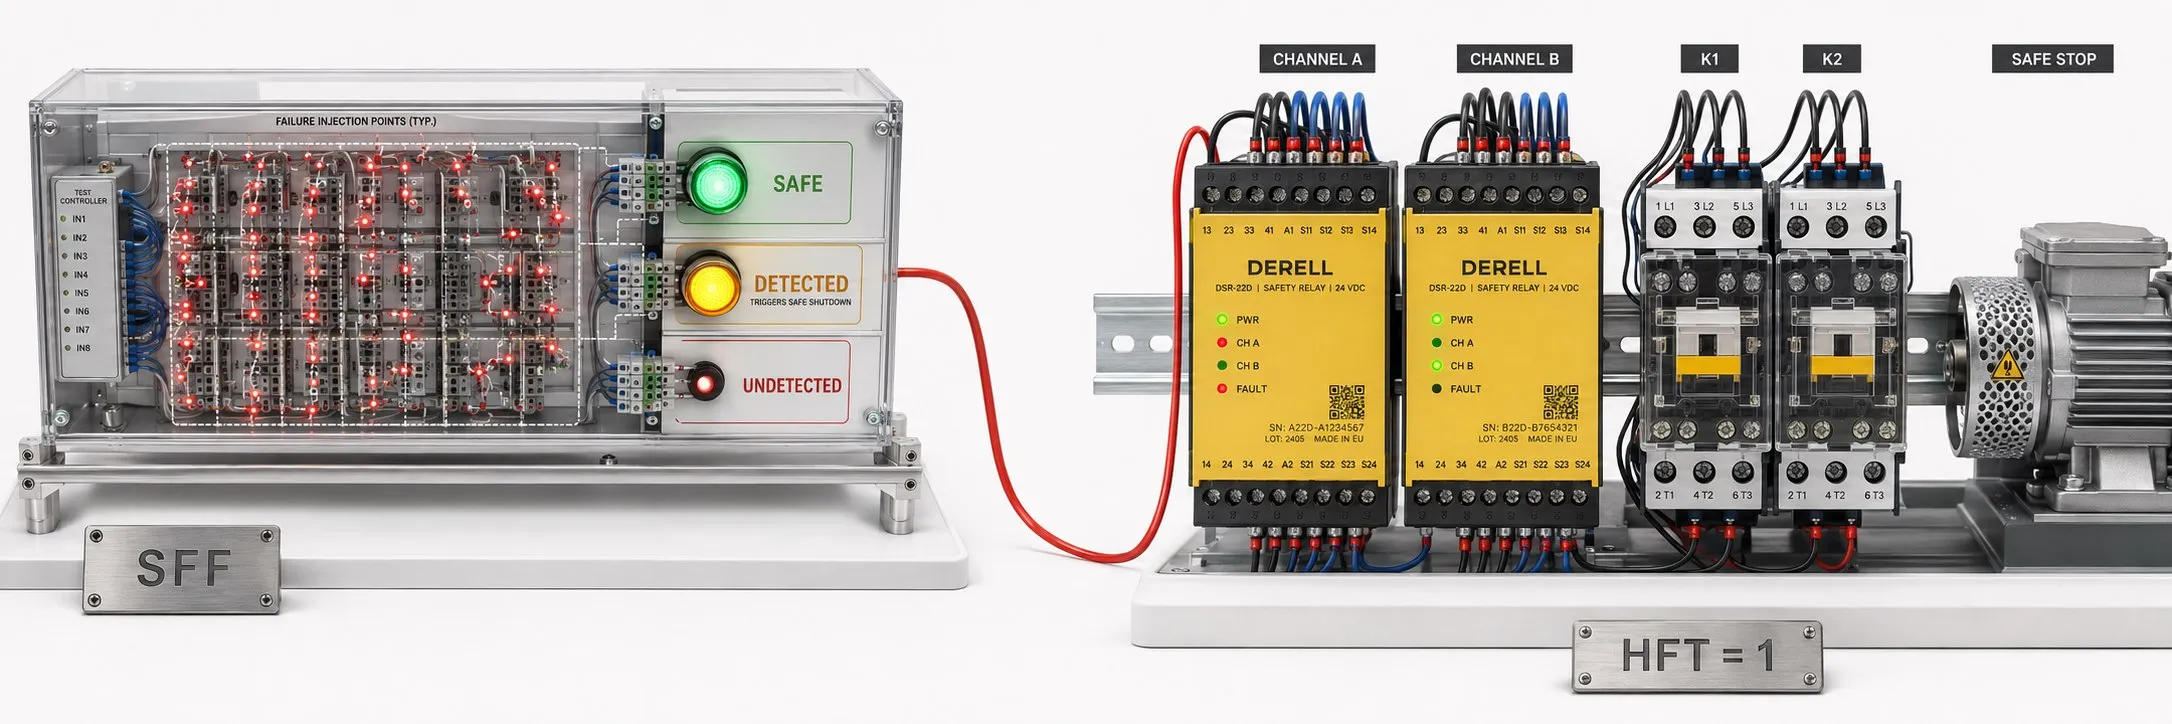
What are SFF and HFT? SFF (Safe Failure Fraction) and HFT (Hardware Fault Tolerance) are important concepts used within the IEC 61508 functional-safety framework to evaluate the failure behaviour and architectural capability of hardware used in a safety-related system.
They do not describe the same property. SFF is concerned with how failures are divided between safe failures, detected dangerous failures and undetected dangerous failures. HFT describes how many hardware faults can occur before the required safety function is lost.
A high SFF does not automatically make a system high-SIL, and a high HFT does not prove functional safety by itself. Quantitative dangerous-failure targets, architectural constraints, systematic capability and safety-lifecycle requirements must also be considered.
In Simple Terms: What Are SFF and HFT?
Imagine that ten different hardware faults could occur inside a safety system. If most of those faults either lead to a safe condition or are detected by the system before they become dangerous, the SFF will be relatively high. HFT answers a different question: “If one part fails, can the safety function still do its job?” If one hardware fault can occur without losing the required safety function, the architecture may have HFT 1. In simple terms, SFF looks at what kind of faults occur; HFT looks at how many faults the hardware architecture can tolerate.
What Is SFF – Safe Failure Fraction?
Safe Failure Fraction expresses the fraction of the relevant hardware failure rate that consists of safe failures and dangerous failures detected by automatic diagnostics.
It is therefore misleading to describe SFF simply as “the probability that a device fails safely.” SFF also includes dangerous failures that are detected before they can remain hidden in the safety function.
A simplified expression is:
SFF = (λS + λDD) / (λS + λDD + λDU)
where:
λS = safe failure rate
λDD = dangerous detected failure rate
λDU = dangerous undetected failure rate
As SFF increases, the proportion of relevant failures that remain dangerous and undetected becomes smaller. This is important because a dangerous undetected failure can leave a safety function unavailable while the equipment still appears to be operating normally.
What Is a Safe Failure?
A safe failure is a failure that does not result in the loss of the required safety function or that moves the equipment toward a defined safe condition.
For example, in a particular application, loss of power to an energise-to-run safety relay may cause its safety outputs to open and remove hazardous motion. That failure can therefore have a safe effect.
However, whether a failure is classified as safe or dangerous depends on the defined safety function. The same physical failure can have different consequences in different applications.
What Are Dangerous Detected and Dangerous Undetected Failures?
Dangerous Detected (DD) describes a failure that can prevent the required safety action but is detected by the automatic diagnostic mechanisms.
Dangerous Undetected (DU) describes a failure that can prevent the safety function from operating correctly and remains hidden from the normal diagnostics.
Dangerous undetected failures are particularly important because the system may continue to appear healthy until the safety function is actually demanded.
For low-demand safety functions, λDU is also an important contributor to PFDavg – Average Probability of Dangerous Failure on Demand.
What Does an SFF of 90% Mean?
In a simplified example, an SFF of 90% means that 90% of the relevant failure rate included in the SFF calculation consists of failures that are either safe or dangerous but detected.
It does not mean that the device is “90% safe,” that it has 90% reliability or that it has only a 10% chance of failing.
SFF is a functional-safety failure classification metric, not a general product-quality percentage.
A Simple SFF Calculation Example
Assume the following simplified failure-rate data for a device:
λS = 50 FIT
λDD = 450 FIT
λDU = 50 FIT
The simplified SFF calculation is:
SFF = (50 + 450) / (50 + 450 + 50)
SFF ≈ 90.9%
This indicates that most of the relevant failure rate is classified as safe or dangerous detected. However, the maximum SIL capability of the device cannot be determined from this percentage alone.
What Is HFT – Hardware Fault Tolerance?
HFT stands for Hardware Fault Tolerance. It describes the ability of a hardware subsystem to continue performing the required safety function when a specified number of hardware faults are present.
HFT does not mean “Hardware Detected Fault Tolerance.” It is also not best explained using RAID disks, ECC memory or ordinary computer-data redundancy. Those may be examples of general fault tolerance, but IEC 61508 HFT concerns the architecture of safety-related hardware.
What Does HFT 0 Mean?
HFT 0 means that the hardware architecture has no tolerance to the relevant hardware fault before loss of the required safety function. A single appropriate dangerous hardware fault can therefore be sufficient to cause loss of the safety function.
A simple single-channel arrangement can be conceptually represented as:
1 sensor → 1 logic solver → 1 final element
However, the actual HFT classification must be based on the subsystem architecture and applicable IEC 61508 assessment; it should not be assigned purely from a simplified drawing.
What Does HFT 1 Mean?
HFT 1 means that the required safety function can continue despite one relevant hardware fault. A second appropriate hardware fault may then cause loss of the function.
This capability is often associated with redundant or fault-tolerant architectures, but HFT 1 does not simply mean “install two devices.”
Internal device architecture, independence, diagnostics and common-cause failure must also be considered.
What Does HFT 2 Mean?
HFT 2 means that the hardware architecture can tolerate two relevant hardware faults without losing the required safety function.
Architectures providing HFT 2 can require substantial redundancy and independence. As with HFT 1, the HFT value should not be inferred solely from the visible number of channels or components.
Are HFT and Redundancy the Same Thing?
Not exactly. Redundancy is one engineering method that can be used to achieve fault tolerance. HFT describes the fault-tolerance capability that the hardware architecture actually provides.
For example, two sensors may be installed, but both may depend on the same 24 VDC power supply, share the same cable route or be exposed to the same environmental stress.
This means both channels can potentially fail because of one shared cause. Functional safety therefore also considers Common Cause Failure (CCF).
What Is Diagnostic Coverage?
Diagnostic Coverage (DC) describes how effectively automatic diagnostics detect the relevant failures.
For dangerous failures, a simplified expression is:
DC = λDD / (λDD + λDU)
If 90% of the relevant dangerous failure rate is detected automatically and 10% remains undetected, the dangerous-failure diagnostic coverage is approximately 90%.
It is therefore too broad to say that “90% Diagnostic Coverage means the system detects 90% of every possible fault.” Diagnostic Coverage depends on which failure category, diagnostic mechanism and subsystem are being evaluated.
Are SFF and Diagnostic Coverage the Same?
No. Diagnostic Coverage focuses on the proportion of relevant failures detected by the diagnostic mechanisms.
SFF includes both safe failures and dangerous detected failures. Therefore, two devices can have similar diagnostic coverage but different SFF values because their safe-failure contributions are different.
How Are SFF and HFT Related?
Within IEC 61508 hardware architectural constraints, SFF and HFT can be used together to determine architectural limits on the hardware safety integrity that a subsystem can claim.
In general terms, a subsystem with a larger proportion of dangerous undetected failures may require greater hardware fault tolerance before a higher SIL capability can be supported.
A subsystem with higher SFF has a smaller proportion of dangerous undetected failure rate, but this still does not mean that “SFF = X%, therefore SIL = Y” is universally valid.
The subsystem type, HFT, architectural assessment route, random hardware failure targets and systematic capability must also be considered.
What Is Route 1H?
IEC 61508 provides different approaches for satisfying hardware architectural constraints. One of these is commonly referred to as Route 1H.
Under Route 1H, SFF and HFT are important parameters used to determine the architectural limit for the hardware subsystem.
This is why a functional-safety certificate or safety manual may contain statements similar to “SIL 2 at HFT=0 / SIL 3 at HFT=1 under Route 1H.”
Such a statement does not mean that the device automatically creates a SIL 3 safety function. The actual architecture, PFDavg or PFH, systematic capability and other requirements still have to be satisfied.
What Is Route 2H?
Route 2H provides an alternative path for demonstrating compliance with the IEC 61508 hardware architectural constraints when the required conditions for sufficiently dependable reliability data and field experience are satisfied.
Under this approach, the traditional SFF-based Route 1H table is not the only basis for determining architectural capability; specified minimum HFT and reliability-data conditions become important.
For this reason, modern functional-safety certificates may refer to Route 1H, Route 2H or both. It is therefore incorrect to assume that SFF alone always determines the maximum SIL capability of a component.
What Are Type A and Type B Elements?
IEC 61508 also distinguishes between Type A and Type B hardware elements when applying architectural constraints.
In simplified terms, a Type A element has well-defined failure modes, well-understood failure behaviour and sufficiently dependable failure data. If one or more of the relevant conditions are not satisfied, the element is treated as Type B.
Complex programmable electronic devices and other complex electronic subsystems can therefore require the more demanding Type B considerations.
Type A and Type B are not labels for “good hardware” and “bad hardware.” They are classifications used within the IEC 61508 hardware safety-integrity assessment process.
How Are SFF, HFT and SIL Related?
Determining the Safety Integrity Level of a safety function requires much more than checking an SFF percentage or HFT number.
Depending on the application, the assessment can include:
• PFDavg or PFH target
• Hardware architectural constraints
• Hardware Fault Tolerance
• SFF or the applicable alternative architectural route
• Systematic capability
• Functional-safety lifecycle requirements
Therefore, “SFF is 90%, so the device is SIL 3” is not a technically sufficient conclusion.
Are SFF and PFDavg the Same?
No. PFDavg expresses the average probability that a low-demand safety function will fail dangerously when demanded.
SFF describes how the hardware failure rate is distributed between safe, dangerous detected and dangerous undetected failure categories.
A device may have a high SFF but still contribute too much PFDavg because of its λDU, proof-test interval, architecture or other parameters.
What Is the Relationship Between FMEDA and SFF?
FMEDA – Failure Modes, Effects and Diagnostic Analysis extends traditional failure-mode analysis by including quantitative failure rates and the effectiveness of diagnostic mechanisms.
An FMEDA can classify failures into functional-safety categories and provide values such as λSD, λSU, λDD and λDU.
These failure-rate data can then be used in SFF calculations, PFDavg or PFH calculations and wider hardware safety-integrity assessment.
What Do SFF and HFT Mean for a Safety PLC?
A safety PLC may contain redundant processors, cross-checking, memory tests, watchdogs, I/O diagnostics and other internal safety mechanisms.
These features can help detect dangerous failures and allow the system to respond safely when hardware faults occur.
However, a safety PLC with excellent diagnostic coverage or fault-tolerance capability does not automatically make the complete machine high-SIL. The sensor subsystem, safety logic and final element must all be assessed as part of the complete safety function.
How Do SFF and HFT Apply to Variable Frequency Drives?
Modern variable frequency drives can use dual-channel circuitry, cross-monitoring and automatic diagnostics in functions such as STO – Safe Torque Off.
Functional safety of safety-related power drive systems is addressed within the IEC 61800 series, particularly IEC 61800-5-2.
Drive safety manuals may therefore contain values or statements relating to HFT, PFH, diagnostic test interval, SIL capability and hardware architecture.
Common SFF and HFT Mistakes
Expanding HFT as “Hardware Detected Fault Tolerance”: The correct term is Hardware Fault Tolerance.
Treating SFF as a reliability percentage: SFF is not a product-quality or uptime percentage.
Treating Diagnostic Coverage and SFF as the same metric: Diagnostic Coverage concerns detected failures, while SFF also includes safe failures.
Assuming high SFF automatically means high SIL: HFT, PFDavg or PFH, systematic capability and other requirements must also be satisfied.
Assuming two channels automatically mean HFT 1: Architecture, independence and common-cause failure must be evaluated.
Using RAID or ECC as the main HFT explanation: Those are general computing fault-tolerance examples, not the correct foundation for explaining IEC 61508 hardware fault tolerance.
Why Are SFF and HFT Important?
Functional safety cannot be evaluated by asking only, “How often does this device fail?” Engineers also need to ask how the device fails, whether a dangerous failure will be detected and whether the safety function can continue when hardware faults occur.
SFF helps describe the failure behaviour. HFT helps describe the ability of the hardware architecture to tolerate faults.
Functional safety does not assume that hardware will never fail. It assumes that failures will eventually occur and designs the system so those failures do not create unacceptable risk.
Where Should an SFF, HFT and SIL Assessment Start?
The correct process does not start by looking at an SFF percentage and choosing a SIL.
Identify the hazard → assess the risk → define the required safety function → determine the required SIL → select the architecture and devices → evaluate failure rates and diagnostics → verify HFT and architectural constraints → calculate PFDavg or PFH → validate the complete safety function.
This approach forms part of the broader functional-safety process used in industrial automation, safety PLC applications, process safety and machinery safety.
Important: SFF, HFT and Diagnostic Coverage are different concepts. None of them alone proves the SIL of a safety function. Hardware architecture, random hardware failure performance, systematic capability and the complete functional-safety lifecycle must be considered together.
SIL Topic Guide
What Is SIL? • PFDavg • SIL 1 • SIL 2 • SIL 3 • SIL 4
Related Standards and Automation Guides
Industrial Standards • IEC Standards • Machinery Safety • IEC 61800 • Safe Torque Off (STO)
Industrial Automation • What Is Automation? • PLC & HMI • Device Standards